Data protection
Privacy policy
Version:
Introduction and overview
We have written this privacy policy (version 09.10.2026-113240972) to explain to you, in accordance with the requirements of the General Data Protection Regulation (EU) 2016/679 and applicable national laws, which personal data (referred to as data for short) we, as the controller — and the processors commissioned by us (e.g. providers) — process, will process in the future, and what lawful options you have. The terms used are to be understood as gender-neutral.
In brief: We provide you with comprehensive information about the data we process about you.
Privacy policies usually sound very technical and use specialist legal terms. This privacy policy, however, aims to describe the most important things to you as simply and transparently as possible. Where this promotes transparency, technical terms are explained in a reader-friendly way, links to further information are provided and graphics are used. In this way, we explain in clear and simple language that, in the course of our business activities, we only process personal data if there is an appropriate legal basis. This is certainly not possible if explanations are as brief, unclear and legally technical as possible, as is often standard on the internet when it comes to data protection. I hope you find the following explanations interesting and informative, and perhaps they include one or two pieces of information you did not already know.
If you still have questions, please contact the responsible body named below or in the legal notice, follow the links provided and consult further information on third-party websites. Our contact details can, of course, also be found in the legal notice.
Scope
This privacy policy applies to all personal data processed by us within the company and to all personal data processed by companies commissioned by us (processors). By personal data, we mean information within the meaning of Article 4(1) GDPR, such as a person's name, email address and postal address. Processing personal data enables us to offer and invoice our services and products, whether online or offline. The scope of this privacy policy includes:
- all online presences (websites, online shops) that we operate
- social media presences and email communication
- mobile apps for smartphones and other devices
In brief: This privacy policy applies to all areas in which personal data is processed in a structured manner within the company through the channels mentioned. If we enter into legal relationships with you outside these channels, we will inform you separately where appropriate.
Legal bases
In the following privacy policy, we provide transparent information about the legal principles and provisions, that is, the legal bases of the General Data Protection Regulation, that allow us to process personal data.
As regards EU law, we refer to REGULATION (EU) 2016/679 OF THE EUROPEAN PARLIAMENT AND OF THE COUNCIL of 27 April 2016. You can, of course, read this EU General Data Protection Regulation online on EUR-Lex, the access point to EU law, at https://eur-lex.europa.eu/legal-content/DE/ALL/?uri=celex%3A32016R0679.
We only process your data if at least one of the following conditions applies:
- Consent (Article 6(1)(a) GDPR): You have given us your consent to process data for a particular purpose. An example would be storing the data you entered in a contact form.
- Contract (Article 6(1)(b) GDPR): We process your data to fulfil a contract or pre-contractual obligations with you. If, for example, we enter into a purchase contract with you, we need personal information beforehand.
- Legal obligation (Article 6(1)(c) GDPR): We process your data if we are subject to a legal obligation. For example, we are legally required to retain invoices for accounting purposes. These usually contain personal data.
- Legitimate interests (Article 6(1)(f) GDPR): In the case of legitimate interests that do not restrict your fundamental rights, we reserve the right to process personal data. For example, we need to process certain data to operate our website securely and in an economically efficient manner. This processing therefore constitutes a legitimate interest.
Other conditions, such as performing tasks in the public interest, exercising official authority or protecting vital interests, do not usually apply to us. If such a legal basis should nevertheless be relevant, it will be stated in the appropriate section.
In addition to the EU Regulation, national laws also apply:
- In Austria, this is the Federal Act concerning the Protection of Natural Persons with regard to the Processing of Personal Data (Data Protection Act), abbreviated to DSG.
- In Germany, the Federal Data Protection Act, abbreviated to BDSG, applies.
If further regional or national laws apply, we will inform you about them in the following sections.
Contact details of the controller
If you have questions about data protection or the processing of personal data, you will find below the contact details of the controller in accordance with Article 4(7) of the EU General Data Protection Regulation (GDPR):
Koegel-Tec defence GmbH
Dorf 13
A-6345 Kössen
Austria
Authorised representative: Gundhard Kögel
Email: [email protected]
Legal notice: https://koegel-tec.com/imprint.html
Retention period
Our general criterion is that we only retain personal data for as long as is absolutely necessary to provide our services and products. This means that we delete personal data as soon as the reason for processing the data no longer exists. In some cases, we are legally required to retain certain data even after the original purpose no longer applies, for example for accounting purposes.
If you wish to have your data deleted or withdraw your consent to data processing, the data will be deleted as quickly as possible, provided there is no obligation to retain it.
We provide information below about the specific duration of the respective data processing where we have further information about it.
Rights under the General Data Protection Regulation
In accordance with Articles 13 and 14 GDPR, we inform you about the following rights to which you are entitled, so that data is processed fairly and transparently:
- Under Article 15 GDPR, you have the right to obtain information about whether we process data about you. If this is the case, you have the right to receive a copy of the data and the following information:
- the purpose for which we carry out the processing;
- the categories, that is, the types of data being processed;
- who receives this data and, if the data is transferred to third countries, how security can be guaranteed;
- how long the data is retained;
- the existence of the right to rectification, erasure or restriction of processing and the right to object to processing;
- that you can lodge a complaint with a supervisory authority (you will find links to these authorities below);
- the origin of the data if we did not collect it from you;
- whether profiling is carried out, that is, whether data is automatically evaluated to create a personal profile of you.
- Under Article 16 GDPR, you have the right to rectification of the data, which means that we must correct data if you find errors.
- Under Article 17 GDPR, you have the right to erasure (the “right to be forgotten”), which specifically means that you may request the deletion of your data.
- Under Article 18 GDPR, you have the right to restriction of processing, which means that we may only retain the data and may no longer use it.
- Under Article 20 GDPR, you have the right to data portability, which means that we will provide your data to you in a commonly used format upon request.
- Under Article 21 GDPR, you have the right to object, which, once enforced, results in a change to the processing.
- If the processing of your data is based on Article 6(1)(e) (public interest, exercise of official authority) or Article 6(1)(f) (legitimate interests), you may object to the processing. We will then examine as quickly as possible whether we can legally comply with this objection.
- If data is used for direct advertising, you may object to this type of data processing at any time. We may then no longer use your data for direct marketing.
- If data is used for profiling, you may object to this type of data processing at any time. We may then no longer use your data for profiling.
- Under Article 22 GDPR, you have, under certain circumstances, the right not to be subject to a decision based solely on automated processing (for example, profiling).
- Under Article 77 GDPR, you have the right to lodge a complaint. This means that you may complain to the data protection authority at any time if you believe that the processing of personal data infringes the GDPR.
In brief: You have rights — do not hesitate to contact the responsible body at our company listed above!
If you believe that the processing of your data infringes data protection law or that your data protection rights have otherwise been violated, you may lodge a complaint with the supervisory authority. In Austria, this is the Data Protection Authority, whose website can be found at https://www.dsb.gv.at/. In Germany, there is a data protection commissioner for each federal state. For more information, you can contact the Federal Commissioner for Data Protection and Freedom of Information (BfDI). The following local data protection authority is responsible for our company:
Austrian Data Protection Authority
Head: Dr. Matthias Schmidl
Address: Barichgasse 40-42, 1030 Vienna
Telephone: +43 1 52 152-0
Email address: [email protected]
Website: https://www.dsb.gv.at/
Security of data processing
To protect personal data, we have implemented both technical and organisational measures. Wherever possible, we encrypt or pseudonymise personal data. In this way, within the scope of our capabilities, we make it as difficult as possible for third parties to infer personal information from our data.
Article 25 GDPR refers here to “data protection by design and by default” and means that security must always be considered and appropriate measures taken, both for software (e.g. forms) and hardware (e.g. access to the server room). Below, where necessary, we discuss specific measures in more detail.
TLS encryption with https
TLS, encryption and https sound very technical, and they are. We use HTTPS (Hypertext Transfer Protocol Secure, meaning “secure hypertext transfer protocol”) to transmit data over the internet in a manner protected against eavesdropping.
This means that the entire transmission of all data from your browser to our web server is secured — nobody can “listen in”.
We have therefore introduced an additional layer of security and fulfil data protection by design (Article 25(1) GDPR). By using TLS (Transport Layer Security), an encryption protocol for secure data transmission over the internet, we can ensure the protection of confidential data.
You can recognise the use of this protection for data transmission by the small padlock symbol  at the top left of your browser, to the left of the internet address (e.g. examplepage.com), and the use of the https scheme (instead of http) as part of our internet address.
If you would like to know more about encryption, we recommend a Google search for “Hypertext Transfer Protocol Secure wiki” to find useful links to further information.
Communication
| Communication summary 👥 Data subjects: Everyone who communicates with us by telephone, email or online form 📓 Data processed: e.g. telephone number, name, email address, form data entered. You will find more details under the respective type of contact used 🤝 Purpose: Handling communication with customers, business partners, etc. 📅 Retention period: Duration of the business matter and statutory requirements ⚖️ Legal bases: Article 6(1)(a) GDPR (consent), Article 6(1)(b) GDPR (contract), Article 6(1)(f) GDPR (legitimate interests) |
If you contact us and communicate by telephone, email or online form, personal data may be processed.
The data is processed to handle and deal with your question and the related business transaction. The data is retained for this duration or for as long as the law requires.
Data subjects
The processes mentioned affect everyone who seeks to contact us through the communication channels we provide.
Telephone
If you call us, the call data is stored in pseudonymised form on the respective device and by the telecommunications provider used. In addition, data such as your name and telephone number may subsequently be sent by email and stored to answer your enquiry. The data is deleted as soon as the business matter has been concluded and statutory requirements allow it.
If you communicate with us by email, data may be stored on the respective device (computer, laptop, smartphone, etc.), and data is stored on the email server. The data is deleted as soon as the business matter has been concluded and statutory requirements allow it.
Online forms
If you communicate with us through an online form, data is stored on our web server and may be forwarded to one of our email addresses. The data is deleted as soon as the business matter has been concluded and statutory requirements allow it.
Legal bases
Processing the data is based on the following legal bases:
- Article 6(1)(a) GDPR (consent): You give us consent to store your data and continue to use it for purposes relating to the business matter;
- Article 6(1)(b) GDPR (contract): Processing is necessary to fulfil a contract with you or a processor, such as the telephone provider, or we must process the data for pre-contractual activities, such as preparing a quotation;
- Article 6(1)(f) GDPR (legitimate interests): We want to handle customer enquiries and business communication in a professional manner. Certain technical facilities, such as email programs, Exchange servers and mobile network operators, are necessary for us to conduct communication efficiently.
Cookies
| Cookies summary 👥 Data subjects: Visitors to the website 🤝 Purpose: Depends on the respective cookie. You will find more details below or from the manufacturer of the software that sets the cookie. 📓 Data processed: Depends on the respective cookie used. You will find more details below or from the manufacturer of the software that sets the cookie. 📅 Retention period: Depends on the respective cookie and can vary from hours to years ⚖️ Legal bases: Article 6(1)(a) GDPR (consent), Article 6(1)(f) GDPR (legitimate interests) |
What are cookies?
Our website uses HTTP cookies to store user-specific data.
Below, we explain what cookies are and why they are used, so that you can better understand the following privacy policy.
Whenever you browse the internet, you use a browser. Well-known browsers include Chrome, Safari, Firefox, Internet Explorer and Microsoft Edge. Most websites store small text files in your browser. These files are called cookies.
One thing cannot be denied: cookies are really useful little helpers. Almost all websites use cookies. More precisely, they are HTTP cookies, as there are other cookies for other areas of application. HTTP cookies are small files stored on your computer by our website. These cookie files are automatically placed in the cookie folder, effectively the “brain” of your browser. A cookie consists of a name and a value. When defining a cookie, one or more attributes must also be specified.
Cookies store certain user data about you, such as your language or personal page settings. When you return to our website, your browser sends the “user-related” information back to our website. Thanks to cookies, our website knows who you are and offers you the settings you are used to. In some browsers, each cookie has its own file; in others, such as Firefox, all cookies are stored in a single file.
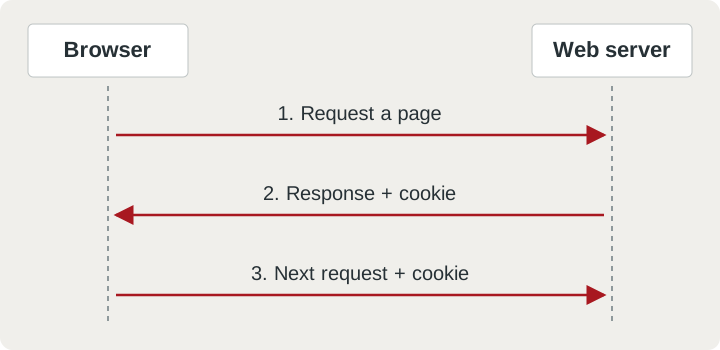
The following graphic shows a possible interaction between a web browser, such as Chrome, and the web server. The web browser requests a website and receives a cookie back from the server, which the browser uses again as soon as another page is requested.
There are both first-party cookies and third-party cookies. First-party cookies are created directly by our website, while third-party cookies are created by partner websites (e.g. Google Analytics). Each cookie must be assessed individually, as each cookie stores different data. A cookie's expiry time also varies from a few minutes to a few years. Cookies are not software programs and do not contain viruses, Trojans or other “malware”. Cookies also cannot access information on your PC.
Cookie data may, for example, look like this:
Name: _ga
Value: GA1.2.1326744211.152113240972-9
Purpose: Distinguishing website visitors
Expiry date: After 2 years
A browser should be able to support these minimum sizes:
- At least 4096 bytes per cookie
- At least 50 cookies per domain
- At least 3000 cookies in total
What types of cookies are there?
The question of which cookies we specifically use depends on the services used and is explained in the following sections of this privacy policy. At this point, we would like to briefly discuss the different types of HTTP cookies.
Four types of cookies can be distinguished:
Essential cookies
These cookies are necessary to ensure the basic functions of the website. For example, these cookies are needed when a user places a product in the shopping basket, then continues browsing other pages and only goes to the checkout later. These cookies prevent the shopping basket from being deleted, even if the user closes their browser window.
Functional cookies
These cookies collect information about user behaviour and whether the user receives any error messages. These cookies are also used to measure loading time and how the website behaves in different browsers.
Target-oriented cookies
These cookies improve user-friendliness. For example, locations entered, font sizes or form data are stored.
Advertising cookies
These cookies are also called targeting cookies. They are used to deliver individually tailored advertising to the user. This can be very practical, but also very annoying.
Usually, when you visit a website for the first time, you are asked which of these types of cookies you would like to allow. And, of course, this decision is also stored in a cookie.
If you would like to know more about cookies and are comfortable with technical documentation, we recommend https://datatracker.ietf.org/doc/html/rfc6265, the Internet Engineering Task Force (IETF) Request for Comments entitled “HTTP State Management Mechanism”.
Purpose of processing through cookies
The purpose ultimately depends on the respective cookie. You will find more details below or from the manufacturer of the software that sets the cookie.
What data is processed?
Cookies are little helpers for many different tasks. Unfortunately, it is not possible to generalise which data is stored in cookies, but we will inform you about the data processed or stored as part of the following privacy policy.
Retention period of cookies
The retention period depends on the respective cookie and is specified in more detail below. Some cookies are deleted after less than an hour, while others may remain stored on a computer for several years.
You can also influence the retention period yourself. You can manually delete all cookies through your browser at any time (see also “Right to object” below). Furthermore, cookies based on consent are deleted at the latest after you withdraw your consent, without affecting the lawfulness of their storage up to that point.
Right to object — how can I delete cookies?
You decide for yourself how and whether you want to use cookies. Regardless of which service or website the cookies come from, you always have the option of deleting, disabling or only partially allowing cookies. For example, you can block third-party cookies while allowing all other cookies.
If you would like to find out which cookies have been stored in your browser, or if you want to change or delete cookie settings, you can find these options in your browser settings:
Chrome: Delete, enable and manage cookies in Chrome
Safari: Manage cookies and website data in Safari
Firefox: Delete cookies to remove information that websites have stored on your computer
Internet Explorer: Delete and manage cookies
Microsoft Edge: Delete and manage cookies
If you do not want cookies at all, you can configure your browser so that it always informs you when a cookie is about to be set. This allows you to decide for each individual cookie whether to allow it. The procedure varies depending on the browser. The best approach is to search Google for instructions using “delete cookies Chrome” or “disable cookies Chrome” if you use Chrome.
Legal basis
The so-called “Cookie Directives” have existed since 2009. They state that storing cookies requires your consent (Article 6(1)(a) GDPR). However, there are still very different responses to these directives within EU countries. In Austria, this directive was implemented in Section 165(3) of the Telecommunications Act (2021). In Germany, the Cookie Directives were not implemented as national law. Instead, this directive was largely implemented in Section 15(3) of the Telemedia Act (TMG), which has been replaced by the Digital Services Act (DDG) since May 2024.
For strictly necessary cookies, even where there is no consent, there are legitimate interests (Article 6(1)(f) GDPR), which are economic in nature in most cases. We want to give visitors to the website a pleasant user experience, and certain cookies are often absolutely necessary for this.
Where cookies that are not strictly necessary are used, this only happens with your consent. The legal basis in this case is Article 6(1)(a) GDPR.
In the following sections, you will be informed in more detail about the use of cookies where the software used employs cookies.
Introduction to Content Delivery Networks
| Content Delivery Networks privacy policy summary 👥 Data subjects: Visitors to the website 🤝 Purpose: Optimising our service (to make the website load faster) 📓 Data processed: Data such as your IP address You will find more details below and in the individual privacy notices. 📅 Retention period: Data is generally retained until it is no longer needed to provide the service ⚖️ Legal bases: Article 6(1)(a) GDPR (consent), Article 6(1)(f) GDPR (legitimate interests) |
What is a Content Delivery Network?
We use a so-called Content Delivery Network on our website. Such a network is usually referred to simply as a CDN. A CDN helps us load our website quickly and smoothly, regardless of your location. In the process, your personal data is also stored, managed and processed on the servers of the CDN provider used. Below, we discuss the service and its data processing in general in more detail. You will find precise information about the handling of your data in the respective provider's privacy policy.
Every Content Delivery Network (CDN) is a network of regionally distributed servers that are all connected to each other through the internet. Through this network, website content (particularly very large files) can be delivered quickly and smoothly, even during major load peaks. To do this, the CDN creates a copy of our website on its servers. As these servers are distributed around the world, the website can be delivered quickly. Data transmission to your browser is therefore significantly shortened by the CDN.
Why do we use a Content Delivery Network for our website?
A fast-loading website is part of our service. Of course, we know how annoying it is when a website loads at a snail's pace. People usually lose patience and leave before the website has fully loaded. Naturally, we want to avoid this. A fast-loading website is therefore a matter of course in our website offering. With a Content Delivery Network, our website loads significantly faster in your browser. Using a CDN is particularly helpful when you are abroad, because the website is delivered from a server near you.
What data is processed?
If you request a website or website content and it is cached in a CDN, the CDN forwards the request to the server closest to you, which then delivers the content. Content Delivery Networks are designed to allow JavaScript libraries to be downloaded and hosted on npm and GitHub servers. Alternatively, most CDNs can also load WordPress plugins if they are hosted on WordPress.org. Your browser may send personal data to the Content Delivery Network we use. This includes data such as your IP address, browser type, browser version, which web page is loaded, or the time and date of your visit. This data is collected and also stored by the CDN. Whether cookies are used to store data depends on the network used. Please read the privacy notices of the respective service for this information.
Right to object
If you want to prevent this data transfer completely, you can install a JavaScript blocker on your PC (see, for example, https://noscript.net/). Of course, our website can then no longer offer the usual service (such as fast loading speed).
Legal basis
If you have consented to the use of a Content Delivery Network, the legal basis for the corresponding data processing is this consent. Under Article 6(1)(a) GDPR (consent), this consent constitutes the legal basis for processing personal data, as may occur when data is collected by a Content Delivery Network.
We also have a legitimate interest in using a Content Delivery Network to optimise our online service and make it more secure. The corresponding legal basis is Article 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use the tool insofar as you have given your consent.
Information about specific Content Delivery Networks is provided — where available — in the following sections.
Cloudflare privacy policy
| Cloudflare privacy policy summary 👥 Data subjects: Visitors to the website 🤝 Purpose: Optimising our service (to make the website load faster) 📓 Data processed: Data such as IP address, contact and log information, security fingerprints and website performance data You will find more details below in this privacy policy. 📅 Retention period: Data is generally retained for less than 24 hours ⚖️ Legal bases: Article 6(1)(a) GDPR (consent), Article 6(1)(f) GDPR (legitimate interests) |
What is Cloudflare?
We use Cloudflare from Cloudflare, Inc. (101 Townsend St., San Francisco, CA 94107, USA) on this website to make our website faster and more secure. Cloudflare uses cookies and processes user data in doing so. Cloudflare, Inc. is an American company that offers a Content Delivery Network and various security services. These services sit between the user and our hosting provider. Below, we will try to explain in more detail exactly what this means.
A Content Delivery Network (CDN), such as the one provided by Cloudflare, is simply a network of connected servers. Cloudflare has distributed such servers around the world to bring websites to your screen more quickly. Put simply, Cloudflare creates copies of our website and places them on its own servers. When you visit our website, a load-balancing system ensures that the largest parts of our website are delivered by the server that can display our website to you most quickly. A CDN significantly shortens the distance of data transmission to your browser. As a result, Cloudflare delivers our website's content to you from servers around the world, as well as from our hosting server. Cloudflare is particularly helpful for users from abroad, as the page can be delivered from a nearby server. In addition to delivering websites quickly, Cloudflare also offers various security services, such as DDoS protection and a Web Application Firewall.
Why do we use Cloudflare on our website?
Of course, we want to offer you the best possible service with our website. Cloudflare helps us make our website faster and more secure. Cloudflare offers us both web optimisations and security services, such as DDoS protection and a web firewall. These also include a reverse proxy and the Content Delivery Network (CDN). Cloudflare blocks threats and limits abusive bots and crawlers that waste our bandwidth and server resources. By storing our website in local data centres and blocking spam software, Cloudflare enables us to reduce our bandwidth usage by approximately 60%. Providing content through a data centre near you and carrying out certain web optimisations there reduces a website's average loading time by approximately half. According to Cloudflare, the “I'm Under Attack Mode” setting can mitigate further attacks by displaying a JavaScript computational challenge that must be solved before a user can access a website. Overall, this makes our website significantly more efficient and less susceptible to spam or other attacks.
What data does Cloudflare process?
Cloudflare generally only forwards data controlled by website operators. The content is therefore determined by the website operator, rather than by Cloudflare. Cloudflare may also collect certain information about the use of our website and process data sent by us or for which Cloudflare has received appropriate instructions. In most cases, Cloudflare receives data such as IP addresses, contact and log information, security fingerprints and website performance data. Log data helps Cloudflare detect new threats, for example. In this way, Cloudflare can ensure a high level of security for our website. Cloudflare processes this data as part of its services in compliance with applicable laws. These naturally include the General Data Protection Regulation (GDPR). Cloudflare also works with third-party providers. They may only process personal data under Cloudflare's instructions and in accordance with its privacy policies and other confidentiality and security measures. Cloudflare does not disclose personal data without our explicit consent.
How long and where is the data stored?
Cloudflare stores your information mainly in the USA and the European Economic Area. Cloudflare may transfer and access the information described above from anywhere in the world. In general, Cloudflare retains user-level data for domains on the Free, Pro and Business plans for less than 24 hours. For Enterprise domains with Cloudflare Logs (formerly Enterprise LogShare or ELS) enabled, data may be retained for up to 7 days. However, if IP addresses trigger security alerts at Cloudflare, there may be exceptions to the retention periods stated above.
How can I delete my data or prevent data storage?
Cloudflare retains data logs only for as long as necessary, and in most cases this data is deleted again within 24 hours. Cloudflare also does not store personal data, such as your IP address. However, there is information that Cloudflare stores indefinitely as part of its permanent logs to improve the overall performance of Cloudflare Resolver and identify potential security risks. You can read about exactly which permanent logs are stored at https://www.cloudflare.com/application/privacypolicy/. All data collected by Cloudflare (whether temporary or permanent) is stripped of all personal data. Cloudflare also anonymises all permanent logs.
Cloudflare explains in its privacy policy that it is not responsible for the content it receives. If, for example, you ask Cloudflare whether it can update or delete your content, Cloudflare generally refers you to us as the website operator. You can also completely prevent Cloudflare from collecting and processing your data by disabling the execution of script code in your browser or adding a script blocker to your browser.
Legal basis
If you have consented to the use of Cloudflare, the legal basis for the corresponding data processing is this consent. Under Article 6(1)(a) GDPR (consent), this consent constitutes the legal basis for processing personal data, as may occur when data is collected by Cloudflare.
We also have a legitimate interest in using Cloudflare to optimise our online service and make it more secure. The corresponding legal basis is Article 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use Cloudflare insofar as you have given your consent.
Cloudflare also processes data about you in the USA, among other places. Cloudflare is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
Cloudflare also uses so-called Standard Contractual Clauses (= Article 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are templates provided by the European Commission and are intended to ensure that your data complies with European data protection standards even when transferred to third countries (such as the USA) and stored there. Through the EU-US Data Privacy Framework and the Standard Contractual Clauses, Cloudflare undertakes to maintain the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the European Commission. You can find the decision and the corresponding Standard Contractual Clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de.
You can find more information about the Standard Contractual Clauses and the data processed through the use of Cloudflare in the privacy policy at https://www.cloudflare.com/de-de/privacypolicy/.
Explanation of terms used
We always strive to write our privacy policy as clearly and understandably as possible. However, this is not always easy, particularly with technical and legal topics. It often makes sense to use legal terms (such as personal data) or certain technical expressions (such as cookies or IP address). However, we do not want to use them without an explanation. Below, you will find an alphabetical list of important terms used that we may not yet have explained sufficiently in the preceding privacy policy. If these terms have been taken from the GDPR and are definitions, we will also quote the GDPR wording here and, where appropriate, add our own explanations.
Processor
Definition under Article 4 GDPR
For the purposes of this Regulation, the term means:
“Processor” means a natural or legal person, public authority, agency or other body which processes personal data on behalf of the controller;
Explanation: As a company and website owner, we are responsible for all data about you that we process. In addition to controllers, there may also be so-called processors. These include any company or person that processes personal data on our behalf. Consequently, in addition to service providers such as tax advisers, processors may also include hosting or cloud providers, payment or newsletter providers, or large companies such as Google or Microsoft.
Consent
Definition under Article 4 GDPR
For the purposes of this Regulation, the term means:
“Consent” of the data subject means any freely given, specific, informed and unambiguous indication of the data subject's wishes by which they, by a statement or by a clear affirmative action, signify agreement to the processing of personal data relating to them;
Explanation: On websites, such consent is generally given through a cookie consent tool. You are probably familiar with this. Whenever you visit a website for the first time, you are usually asked through a banner whether you agree or consent to data processing. Usually, you can also make individual settings and decide for yourself which data processing you allow and which you do not. If you do not consent, no personal data about you may be processed. In principle, consent can, of course, also be given in writing, rather than through a tool.
Personal data
Definition under Article 4 GDPR
For the purposes of this Regulation, the term means:
“Personal data” means any information relating to an identified or identifiable natural person (hereinafter “data subject”); an identifiable natural person is one who can be identified, directly or indirectly, in particular by reference to an identifier such as a name, an identification number, location data, an online identifier or to one or more factors specific to the physical, physiological, genetic, mental, economic, cultural or social identity of that natural person;
Explanation: Personal data is therefore all data that can identify you as a person. This generally includes data such as:
- Name
- Address
- Email address
- Postal address
- Telephone number
- Date of birth
- Identification numbers, such as a social security number, tax identification number, identity card number or student registration number
- Banking data, such as account number, credit information, account balances and much more
According to the Court of Justice of the European Union (CJEU), your IP address also constitutes personal data. IT experts can use your IP address to determine at least the approximate location of your device and subsequently identify you as the subscriber. Storing an IP address therefore also requires a legal basis within the meaning of the GDPR. There are also so-called “special categories” of personal data that require particular protection. These include:
- racial and ethnic origin
- political opinions
- religious or philosophical beliefs
- trade union membership
- genetic data, such as data obtained from blood or saliva samples
- biometric data (information about mental, physical or behavioural characteristics that can identify a person).
Health data - data concerning sexual orientation or sex life
Profiling
Definition under Article 4 GDPR
For the purposes of this Regulation, the term means:
“Profiling” means any form of automated processing of personal data consisting of the use of personal data to evaluate certain personal aspects relating to a natural person, in particular to analyse or predict aspects concerning that natural person's performance at work, economic situation, health, personal preferences, interests, reliability, behaviour, location or movements;
Explanation: Profiling brings together various pieces of information about a person to learn more about that person. On the web, profiling is frequently used for advertising purposes or credit checks. Web or advertising analytics programs, for example, collect data about your behaviour and interests on a website. This produces a specific user profile, which can be used to deliver advertising to a particular target group.
Controller
Definition under Article 4 GDPR
For the purposes of this Regulation, the term means:
“Controller” means the natural or legal person, public authority, agency or other body which, alone or jointly with others, determines the purposes and means of the processing of personal data; where the purposes and means of such processing are determined by Union or Member State law, the controller or the specific criteria for its nomination may be provided for by Union or Member State law;
Explanation: In our case, we are responsible for processing your personal data and are consequently the “controller”. If we pass on collected data to other service providers for processing, they are “processors”. A “data processing agreement” (Auftragsverarbeitungsvertrag, AVV) must be signed for this purpose.
Processing
Definition under Article 4 GDPR
For the purposes of this Regulation, the term means:
“Processing” means any operation or set of operations which is performed on personal data or on sets of personal data, whether or not by automated means, such as collection, recording, organisation, structuring, storage, adaptation or alteration, retrieval, consultation, use, disclosure by transmission, dissemination or otherwise making available, alignment or combination, restriction, erasure or destruction;
Note: When we refer to processing in our privacy policy, we mean any type of data processing. As mentioned above in the original GDPR explanation, this includes storing and processing data, as well as collecting it.
All texts are protected by copyright.
Source: Privacy policy created with the Privacy Policy Generator for Austria by AdSimple